Anthropic September 2026 Threat Intelligence Report: detecting and countering AI misuse
- ID: 348626d9
- 原文链接: https://www.anthropic.com/threat-intelligence-report-september-2026
- 作者: Anthropic Threat Intelligence
- 日期: 2026-09-10
- 平台: anthropic
- 来源类型: article
- 标签: anthropic, threat-intelligence, ai-misuse, cybersecurity, distillation, safety, field-note
- 质量评分: 4/5
- 抓取时间: 2026-09-11T15:54:30+00:00
- 抓取状态: ok
中文导读
Anthropic 2026-09 威胁情报报告披露其在 2025-12 至 2026-08 间识别并打断的 AI 滥用案例,覆盖网络行动监控影响行动常规武器生物滥用诈骗和非法蒸馏七类危害报告称 Claude Haiku/Sonnet/Opus 被用于从侦察工具开发到数据处理的多阶段流程,且 Sophisticated attacks no longer require sophisticated attackers;后半部分还披露多家中国实验室和代理网络围绕 Claude 的蒸馏转发和数据采集需按厂商单方披露阅读
为什么值得关注
这份报告把 AI 滥用从提示词越狱推到真实行动链:网络行动诈骗监控与蒸馏都开始被 agent 工作流放大
English summary
Anthropics September 2026 threat-intelligence report covers operations disrupted from Dec 2025 through Aug 2026 across cyber operations, surveillance, influence, conventional weapons, biological misuse, scams/fraud and illicit distillation. It argues that AI collapses labor and tooling gaps across the cyber kill chain and documents notable cases including Russian espionage workflows, scam networks and alleged frontier-model distillation campaigns.
图片
- https://www.anthropic.com/_next/image?url=https%3A%2F%2Fwww-cdn.anthropic.com%2Fimages%2F4zrzovbb%2Fwebsite%2Ffc8ef227f64c039d99e27145fae5204fd8a81501-1920x312.jpg&w=3840&q=75
- https://www-cdn.anthropic.com/images/4zrzovbb/website/1c3e87fd90491089b2971dc34f9f75bb8a80f713-1000x1000.svg
抓取内容(opencli-first)
Countering misuse of AI: September 2026 / Anthropic
作者: @AnthropicAI
原文链接: https://www.anthropic.com/threat-intelligence-report-september-2026
Detecting and countering misuse of AI: September 2026
Cyber operations
Read more
Surveillance operations
Read more
Influence operations
Read more
Conventional weapons
Read more
Biological misuse
Read more
Scams and fraud
Read more
Illicit distillation
Read more
Over the past eight months, our Threat Intelligence team identified and disrupted operations in which threat actors tried to use Claude for malicious activity. In this report, we share case studies from those operations and describe how malicious use of Claude has evolved since our previous threat reports in March, August, and November 2025. In each case, we disrupted the activity, used what we learned to strengthen our safeguards, and shared intelligence with authorities and industry partners, where appropriate.
This report covers activity we disrupted between December 2025 and August 2026 across seven harm areas: cyber operations, influence operations, surveillance, scams and fraud, biological misuse, conventional weapons development, and distillation. Claude Haiku, Sonnet, and Opus models were used. None of the misuse cases involved the use of Claude Fable or Mythos-class models, with the exception of one illicit distillation case.
The cases we share here aren’t typical misuse, but rather examples of the most notable and novel threat activity we’ve identified to date. We’re publishing this work because we believe we have a responsibility to disclose malicious misuse of our services. As models become increasingly capable, their risks will increase, unless AI developers and society’s defenders act to make them safer.
The threat actors covered in this report include suspected state-sponsored groups, financially motivated criminals, commercial spyware vendors, state propaganda institutions, and politically motivated individuals. The cases range from a network of fake dating apps designed to defraud users to surveillance systems built to identify and monitor dissidents.
Sophisticated and persistent threat actors continuously test our safeguards and try to circumvent the technical measures we use to detect and prevent misuse. We’ll continue to evolve our safeguards and coordinate with our partners to improve our ability to detect, disrupt, and prevent future misuse.
We hope that the findings in this report will help other developers recognize similar patterns on their own platforms, give governments and civil society a clearer view of how emerging threats take shape, and strengthen collective defenses.
AI-augmented cyber operations
Cyber operations: From assistant to orchestrator
Over the past six months, our Threat Intelligence team identified and disrupted a series of cyber operations in which threat actors used Claude. The actors included suspected state-sponsored groups, financially motivated criminals, and politically motivated individuals. This section presents some of those cases.
Throughout these case studies, the report will reference Generative Threat Groups (GTGs). These are Anthropic’s internal designators for actors observed to be abusing AI. The report also attempts to measure uplift, a term we use to describe the AI capability boost, or how much more harm was caused with AI versus without AI. We view uplift through the lens of speed, scale, and depth, and attempt to determine how an actor’s adoption of AI meaningfully impacts each of these traits.
Many commentators focus on the risk of AI developing exploits at scale. While this is a danger, the risk from AI adoption is more pronounced across the cyber kill chain, where adversaries can operate faster, across a broader and deeper surface area, with fewer resources.
The cases span the period from December 2025 through August 2026. In all cases, Claude Haiku, Sonnet, and Opus models were used; no malicious activity was found on Claude Fable or Mythos (which has a series of safeguards in place that greatly reduce its ability to perform harmful cyber tasks). In each case we disrupted the activity involved, strengthened our AI safeguards based on what we learned, and shared intelligence with authorities and industry partners where appropriate.
In the following report, we begin by discussing the key trends that we’ve observed in these cyber operations, then move to reporting the case studies and how they highlight those trends.
Trends
Sophisticated attacks no longer require sophisticated attackers
The cybersecurity skills of AI models means that AI has collapsed the labor and tooling gap that used to separate well-resourced, state-sponsored operations from individual operators. In the case studies we report below, a hacktivist using stolen API keys, disparate financially motivated individuals, and a state espionage operator each sustained multi-victim campaigns that, even just a year ago, would have required many skilled operators and specialist knowledge.
For threat intelligence investigators, sophistication has stopped being a reliable signal of who is behind an operation. Every layer of offensive operations has been uplifted by AI, from reconnaissance and tool development to data processing and exploitation. An example of this uplift in capabilities is documented in case study GTG-50014 (described below). The net effect of this uplift in capabilities is access to an increased _breadth_ and _depth_ of knowledge, which in turn drives _increased speed_ of capability development and implementation.
In November 2025, we documented an operating model used by a suspected state-sponsored campaign to carry out autonomous attacks. That operating model has now proliferated across every class of actors we investigated. Publicly available offensive agent frameworks, like PentAGI, reproduce much of the same scaffolding for anyone who downloads them. This scaffolding effectively automates each step of the cyber kill chain. The operators behind observed cases range from state services to lone individuals, across a widening set of countries. An example of this adoption of AI-enabled kill chains is documented in case study GTG-20006. As models continue to evolve and improve, we assess that more actors, from lone wolves to organized entities, will continue to adopt AI frameworks to enable more sophisticated cyber attacks at greater speed and scale.
AI’s role in cyber operations has become increasingly autonomous
A majority of the operations described in this report were enabled by AI via direct execution or orchestration. The use of AI went beyond simple questions and responses from a chatbot but rather involved the use of multi-agent frameworks executing reconnaissance, exploitation, and data exfiltration. Humans remained in the loop by setting the targets of attacks and reviewing exfiltration. An example of this trend is GTG-20006. This actor developed an AI-assisted workflow that automatically rebuilt and re-deployed their toolkit if it was detected by security products.
GTG-20006: Russian espionage
Historically, cyber espionage actors have followed a pattern of developing and deploying custom toolkits designed to evade detections. Actors would use these tools until defenders identified and built signatures to detect and block them, and there would then begin a new cycle of evasion and detection. Robust defenses and detections therefore created increased costs for adversaries. Now, however, the adoption of AI threatens to quickly and easily subvert defenders’ ability to impose costs on adversaries via static detections alone.
GTG-20006 is an actor who has increased their speed by automating their operations using AI. Our attribution is consistent with public reporting linking the actor to Midnight Blizzard. One of the operators is a Russian speaker using the handle “JackPoterz” whose tradecraft and targeting are consistent with Russian state-nexus espionage. They ran operations attacking military intelligence targets in Ukrainian and European governments, as well as diplomatic and defense organizations and individuals connected to US foreign policy. We observed GTG-20006 operate through customized AI-driven workflows that automated much of their operations from development, infrastructure acquisition, phishing, persistence through command and control, to data exfiltration.
GTG-20006 employed a custom toolkit composed of two families of Windows-based implants, a mobile exploitation kit, a credential stealing tool that targets browser password stores, a phishing platform designed to mimic priority targets like government organizations, and an administrative console used to manage compromised accounts. Each of these tools was managed and re-tooled as needed during the cyber operations through AI-assisted workflows.
The actor also used AI to monitor how well their tools evaded detections from known security defenses. If their monitoring AI agents identified that any of their deployed malware was detected by a security product, agents would then set about the process of autonomously modifying and rebuilding the malware to evade the existing detections. The agents were designed to continue iterating on GTG-20006’s toolkit until it was undetected. At that point, the tools were staged for live operations from disposable hosting servers where victim traffic was directed to retrieve the malware during their many cyber operations, including phishing, ClickFix, and DNS hijacking schemes.
The actor also used AI to drive their phishing operations. They developed AI-driven workflows to research then register domains and then configure the hosting infrastructure used to send phishing emails. Additional workflows were developed to send the emails and monitor the C2 channels for successful compromises. The human actor engaged primarily to modify Claude Code skills that drove the workflows when they needed to be refined.
Our investigation identified more than 20 distinct organizations targeted in the actor’s operational planning, reconnaissance, and live operations. They included government ministries, defense and intelligence bodies, embassies and diplomatic missions, think tanks, and defense-industrial companies, concentrated in Ukraine and Europe but extending to the Middle East and maritime related government agencies in Asia. A common theme of the targeting was Ukraine and military drone technology providers and supply chains. Exceptions included a Southeast Asian government entity relating to maritime shipping and tracking, and a North African government technology authority.
Cyber operations
<video src="https://cdn.sanity.io/files/4zrzovbb/website/15ad203760eed371255de215796dbb5f9f630536.webm" controls></video>
The most commonly recurring targets were members of the Ukrainian government, military, and diplomatic staff. The actor scanned email services and remote access systems across more than two dozen Ukrainian government organizations.
A secondary recurring target for theft was drone supply chain technology. The actor bulk-exported the mailboxes of at least two drone component manufacturers, targeted a military drone maker, and stole a complete proprietary software development kit for a drone vision system. They spent several days reverse-engineering the drone’s vision system, recovering its product architecture, its hardware bill of materials, its supplier dependencies, and details of an unannounced product. Military drone control and AI vision-related firmware appeared to be of particular interest.
Not all targets were direct: to reach their targets indirectly, the actor compromised at least three hospitality vendors that operate hotel guest WiFi. They used compromised admin credentials to modify DNS records so that they pointed to services owned by the actor (a technique known as DNS hijacking). Guests of hotels using the compromised vendors who connected to the hotel WiFi had their traffic, device identifier and IP address sent to the actor’s servers. At that point, ClickFix\-style lures were staged to deliver Windows, Android and iOS malware to the victim’s device. The actor was able to use a combination of guest information stolen from the hotel management systems with the data stolen from individual guests’ devices to focus additional targeting efforts. Particular targets of interest were individuals associated with Ukraine, including government officials and drone manufacturers. Note that in July 2026, Microsoft Threat Intelligence published a report on the method of theft and malware delivery used here, which they referred to as CaptiveCrunch.
The actor also took over victims’ WhatsApp accounts, using a platform of headless browsers to link victim accounts as companion devices. In part by using the WPPConnect open-source WhatsApp automation library, the actor’s configuration suppressed read receipts so victims would not notice while it bulk-exported Russian and Ukrainian language conversations. At least two former high-level Ukrainian officials were targeted in this way.
The actor also targeted surveillance platforms. They found authorization flaws in the application interface of camera streaming services, and from there they enumerated users and harvested tokens that granted them access to the victims’ live camera streams.
The same actor also conducted an intrusion of a North African government technology authority. They stole credentials to a VPN appliance, and used them to take over the organization’s central account server. This allowed them to exfiltrate its full credential database: more than 300,000 national identity records, and the commercial registry data of more than half a million companies operating in the country.
The actor continued to develop a cloud email espionage platform that in part used “Embassy Kit,” the actor’s framework for managing device code phishing, to operate a Microsoft 365 token theft campaign. This platform, which was used to target diplomatic and government personnel, resulted in the access and exfiltration of mail records from at least eight organizations including a national prosecutor office, a military education institute, and a regional intergovernmental organization.
Windows credential stealers were delivered via fake update-themed social engineering lures, alongside companion payloads with full remote access capabilities. These payloads were designed to freeze the victim machine’s security updates, meaning that new malware detection signatures published by security vendors would not be retrieved or run on the victim’s machine.
The actor used AI at every point in their operations:
- Reconnaissance: The actor used AI to fingerprint email and remote access systems and to harvest information from public sources, building target lists for phishing.
- Initial access: The actor used AI to build and operate the platform that ran these cyber intrusion campaigns. The campaign’s primary access technique was a form of device code phishing that abused legitimate sign-in flows for cloud email services (for further details on device code phishing see this post from Microsoft.) The actor used AI to set up the phishing infrastructure and the exploitation tooling, and executed portions of the intrusions directly including running commands against victim systems, harvesting credentials, and moving laterally through networks under the actor’s direction.
- Collection and exfiltration: The actor used AI to perform the extraction and organization of hundreds of gigabytes of stolen data. In some cases, exfiltration was achieved via bulk exports from compromised mailboxes.
- Maintaining access: The actor used AI to assist in maintaining access to compromised accounts and tenants by automating the registration of actor-controlled devices into the victim organization’s tenant.
In on-premises environments, the actor used AI to monitor the stealth and persistence of their implants. When their implants were flagged by security products, the actor used Claude to systematically identify, modify and redeploy the detected artifacts.
The result of the above is that AI has inverted the cost back onto defenders. Previously, defenders might have been able to slow an attacker’s operational tempo via the deployment of a new detection. Now, at least in theory, capable adversaries can “close the loop,” bypassing traditional security detections faster than defenders can develop and deploy them.
The actor’s malware included the following:
- Windows malware: PowerChrome, WUEngine, Shadow C2, MiniPlasma, CloudSyncSvc;
- Android malware: GiftDrop, a rebranded GiftsExpress Android surveillance RAT;
- iOS malware: DarkSword, an iOS exploit chain.
Indicators of compromise
ms365-live[.]com
teams.ms365-live[.]com
m365-owa[.]com
owa-ms365[.]com
ms365-device[.]com
mslivetest.duckdns[.]org
my-invite[.]org
chamber-ua[.]org
chathamhouse[.]eu
ukrinform-share[.]net
104.145.210[.]184
31.57.243[.]154
statistic-ms[.]live
static-ms[.]live
104.194.151[.]133
ad-g[.]org
104.194.159[.]55
docs-viewer[.]org
144.172.114[.]192
wa-connect[.]eu
mygreatmarket[.]org
mygreatmarket[.]com
213.145.86[.]112
2.26.53[.]194
cdncounter[.]net
static.cdncounter[.]net
stuseamandesilt[.]org
api.stuseamandesilt[.]org
cdn.stuseamandesilt[.]org
update.stuseamandesilt[.]org
itechx[.]tel
pdfviewer2024.b-cdn[.]net
meridian-protocol[.]org
meridiangroup-corp[.]com
projectnightcrawler[.]dev
metricwave[.]org
mgsend[.]org
148.135.195[.]111
185.198.234[.]26
185.198.234[.]101
149.54.42[.]106
104.194.149[.]228
38.146.28[.]132
38.146.28[.]75
wa-meeting[.]com
russianearabroad[.]com
russianearabroad[.]org
anna.manager@russianearabroad[.]net
events@embassy-protocol[.]int
msedgeupdate_v3[.]exe
msedgeupdate[.]exe
version[.]dll
WUEngine[.]exe
DiagHost[.]exe
client_20260507093021_4286d211_x64[.]exe
fix_network[.]apk
be99857449d2856dd5a84e21c8a3d5e0e01456adb44062ddec5a6b4970d8d42c
918fa52ae45ed60ba7cc8bdc99c3cbe9ab92e0375ec31fc05d0d4513be11c593
Expand
GTG-50014: ShinyHunters smash-and-grab opportunists
While some cyber threat actors may conduct targeted intrusions, seeking specific information for espionage or other purposes, others are less focused and deliberate in their operations. These opportunistic hackers have historically used broad-based scanning techniques to identify and probe unpatched internet-facing systems, before exploiting these vulnerabilities to compromise or take over the target systems. We’ve identified several advanced threat actors who used AI to uplift their opportunistic criminal activity, using Claude’s capabilities to accelerate their ability to rapidly scan, exploit, and take over target systems.
Opportunistic attacks come in many forms: racing N-day patches for mass exploitation; rummaging through public container stores, code repos, mobile applications, websites and more looking for credentials, tokens, and API keys; mass scan and exploitation of vulnerable internet facing devices; the creation of service accounts on novice service providers with poor security to escape their containers; prompt injection of LiteLLM or OpenClaw deployments; and more.
Many actors scour the internet for ways into networks and services, stealing data for sale and extortion and later reselling access. This was the case before AI. With AI, however, the pre-existing ecosystem of criminal cyber conduct has increased in scale and severity. With AI, diverse target environments are made trivial to understand and adjust to; unique and obscure configurations are made clear and exploitable. The old adage of “security through obscurity” is no longer viable in this new AI-assisted world: everything connected to the internet is a potential target for exploitation.
Once actors gain access, they typically move straight to databases and look for customer data. If the target is a software-as-a-service (SaaS) provider, they often use the stolen data to access the end customers, and make extortion demands, telling the provider that all of their data and their customers’ data will be leaked or sold online if they do not pay.
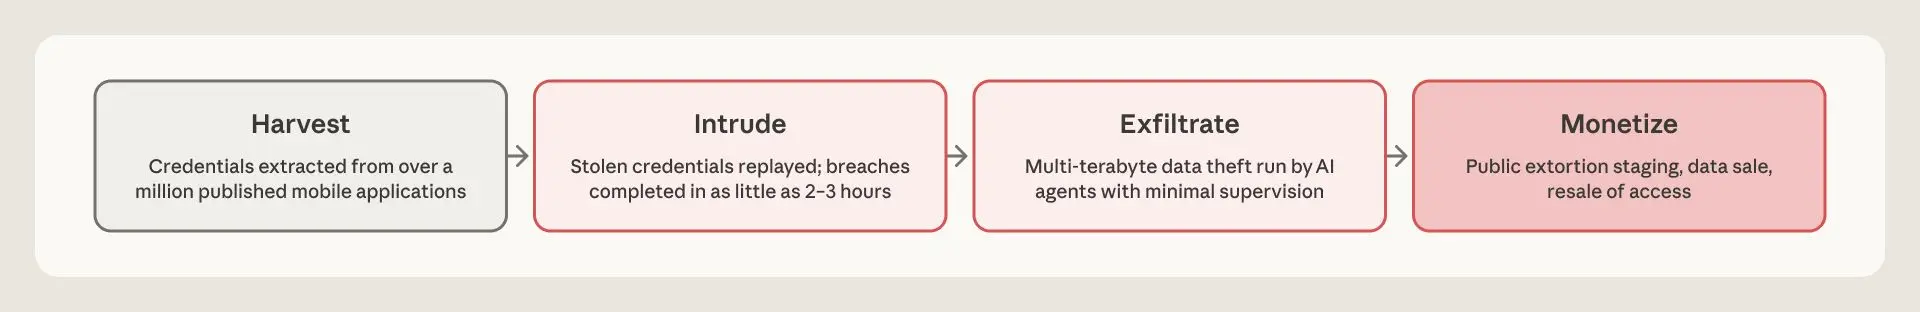
We identified and disrupted multiple clusters of financially motivated cybercrime activity conducted by operators suspected to be affiliates of the ShinyHunters collective, known for several large-scale data theft operations followed by pay-or-leak extortion demands. Although the affiliates appear disparate, and seem to be operating with their own tooling and operational workflows, analysis of their approaches and objectives shows that they are part of the same overall operation.
Figure 1. The attack lifecycle shared by the clusters of suspected ShinyHunters affiliates that we disrupted, from harvesting credentials to extortion.
One French-speaking operator going by the aliases of (MeowSHA | frkoo | blazespider) ran a distributed credential-harvesting pipeline across a fleet of 10 AWS EC2 workers. This pipeline mass-downloaded 1.8 million distinct Android APKs from multiple app-store sources, decompiled them, and scanned for hardcoded secrets with TruffleHog. Verified findings were routed in real time to a Telegram group organized into over 100 source types. A parallel GitHub organization email harvester fed a second stream of stolen GitHub Personal Access Tokens. These two credential pipelines supplied the initial-access credentials
...[truncated for AAIF content file; see source URL for full text]...
om users that accessed Xiaomi’s models through third-party model routing platforms. We have no indication US persons’ data was exposed, but those platforms are commonly accessed by users in the United States and Europe. Those requests to Claude contained the names, contact information, corporate data, and other sensitive data from hundreds of Xiaomi users in at least a dozen languages.
Xiaomi’s illicit distillation campaign leveraged Claude to strengthen training data used for future models. Claude was used to reconstruct the developer environments from exchange transcripts. It also converted multi-turn conversations into cleaner exchanges. Claude was also used to generate both the inputted request and the returned response, mimicking the conversations between a developer and a model. Finally, Xiaomi used Claude to judge the quality of certain answers.
_Scale of distillation attacks attributable to Xiaomi over 20 days in March and April 2026: over 400,000 exchanges observed._
GTG 16012 and GTG 16003: Sensetime, MiniMax, and the third-party reseller ecosystem
The proliferation of proxy services to circumvent Anthropic access restrictions has created a secondary market through which labs can purchase or otherwise acquire harvested exchanges between users and Claude. Some proxy networks both provide Claude access to users in unsupported regions, and also save exchanges in order to sell them to other labs.
For example, SenseTime’s distillation pipeline included transcripts of user exchanges with Claude purchased from third-party data vendors. These exchanges were harvested from users who accessed Claude through intermediaries, like third-party applications or routing services, which logged the transcripts and sold them. SenseTime also used Claude to write the distillation pipeline and to launch and monitor training runs.
MiniMax built its own proxy network service through a shell company. This shell company has no obvious links to MiniMax and does not disclose its relationship to its parent company. This shell proxy network service only offers access to models developed by Anthropic and OpenAI. The service does not offer access to any Chinese models, including Minimax’s own. This evidence suggests that MiniMax established this proxy network service to harvest exchanges between users and US frontier models in order to train its models.
How we address illicit distillation
Distillation is a complex challenge. The entities behind use a range of techniques and systems to access our models and extract their capabilities. No single safeguard can address this issue alone, which is why we use a layered defense to detect and block illicit distillation attacks.
We use metadata and look for signals of irregular activity to identify accounts associated with proxy service networks. Instead of banning proxy accounts individually, we work to attribute this suspicious activity to a specific organization, allowing us to take comprehensive enforcement actions more effectively to prevent distillation attacks.
We’ve also built classifiers designed specifically to detect adversarial extraction. When we are confident that a set of requests are associated with an illicit distillation campaign or other unauthorized use of Claude, we block the request and ban the associated accounts. We strengthened these classifiers earlier this year alongside the launch of Fable 5.
We’ve also added new safeguards that make it harder for unauthorized labs to distill Claude’s capabilities. Claude now summarizes its internal reasoning before responding, which makes stolen transcripts less useful for training another model. And with Fable 5.1 we introduced preserved thinking, which stops new API accounts from altering the system prompt, tools, or messages that precede Claude’s reasoning in multi-turn conversations. That reasoning is encrypted, but editing the context before it is a common technique attackers use to make Claude reveal it.
Finally, when we detect signals of potential abuse, like the unauthorized resale of Claude or accounts operating from unsupported countries like China, Russia, and Iran, our systems can require users to verify their identity to retain access. Accounts that fail to do so are banned.
As we investigate and disrupt distillation attacks, what we learn will continue to inform the safeguards we build.
Back to top
[
The Threat Intelligence team investigates real-world cases of misuse of Claude, and works with the broader Safeguards team to improve our defenses.
Threat Intelligence
](https://www.anthropic.com/threat-intelligence)
Obsidian evidence excerpt
Anthropic 威胁情报报告 2026-09|案例拆解
文件
- [[原始材料]]
- [[报告导读]]
- [[Anthropic-Detecting-and-countering-091026.pdf]]
一句话结论
Anthropic 用七类危害、四十多个案例说明 Claude 在 2025-12 至 2026-08 被怎么滥用、他们怎么打断。材料是单方披露,GTG 是内部编号。
案例
GTG-20006:俄罗斯间谍活动
- 原文:[[案例/01-gtg-20006-russian-espionage/案例原文]]
- 翻译:[[案例/01-gtg-20006-russian-espionage/中文翻译]]
- 背景:[[案例/01-gtg-20006-russian-espionage/案例背景调研]]
- 社交文案(813 字):[[案例/01-gtg-20006-russian-espionage/社交文案]]
- 信息图:![[案例/01-gtg-20006-russian-espionage/gracker信息图-01.png]]
GTG-50014:ShinyHunters 砸抢式机会主义者
- 原文:[[案例/02-gtg-50014-shinyhunters-smash-and-grab-opportunists/案例原文]]
- 翻译:[[案例/02-gtg-50014-shinyhunters-smash-and-grab-opportunists/中文翻译]]
- 背景:[[案例/02-gtg-50014-shinyhunters-smash-and-grab-opportunists/案例背景调研]]
- 社交文案(781 字):[[案例/02-gtg-50014-shinyhunters-smash-and-grab-opportunists/社交文案]]
- 信息图:![[案例/02-gtg-50014-shinyhunters-smash-and-grab-opportunists/gracker信息图-01.png]]
GTG-10007:漏洞利用代工厂与自主攻击框架
- 原文:[[案例/03-gtg-10007-exploit-foundries-and-autonomous-attack-frameworks/案例原文]]
- 翻译:[[案例/03-gtg-10007-exploit-foundries-and-autonomous-attack-frameworks/中文翻译]]
- 背景:[[案例/03-gtg-10007-exploit-foundries-and-autonomous-attack-frameworks/案例背景调研]]
- 社交文案(824 字):[[案例/03-gtg-10007-exploit-foundries-and-autonomous-attack-frameworks/社交文案]]
- 信息图:![[案例/03-gtg-10007-exploit-foundries-and-autonomous-attack-frameworks/gracker信息图-01.png]]
AI 供应链作为目标、赃物和攻击算力
- 原文:[[案例/04-gtg-50021-ai-supply-chain-as-target-loot-and-attack-compute/案例原文]]
- 翻译:[[案例/04-gtg-50021-ai-supply-chain-as-target-loot-and-attack-compute/中文翻译]]
- 背景:[[案例/04-gtg-50021-ai-supply-chain-as-target-loot-and-attack-compute/案例背景调研]]
- 社交文案(797 字):[[案例/04-gtg-50021-ai-supply-chain-as-target-loot-and-attack-compute/社交文案]]
- 信息图:![[案例/04-gtg-50021-ai-supply-chain-as-target-loot-and-attack-compute/gracker信息图-01.png]]
GTG-50020:从酒店预订到 AI 供应链
- 原文:[[案例/05-gtg-50020-from-hotel-bookings-to-the-ai-supply-chain/案例原文]]
- 翻译:[[案例/05-gtg-50020-from-hotel-bookings-to-the-ai-supply-chain/中文翻译]]
- 背景:[[案例/05-gtg-50020-from-hotel-bookings-to-the-ai-supply-chain/案例背景调研]]
- 社交文案(795 字):[[案例/05-gtg-50020-from-hotel-bookings-to-the-ai-supply-chain/社交文案]]
- 信息图:![[案例/05-gtg-50020-from-hotel-bookings-to-the-ai-supply-chain/gracker信息图-01.png]]
GTG-50029:黑客行动主义者针对欧洲政治及相关实体
- 原文:[[案例/06-gtg-50029-hacktivists-targeted-european-political-and-affiliated/案例原文]]
- 翻译:[[案例/06-gtg-50029-hacktivists-targeted-european-political-and-affiliated/中文翻译]]
- 背景:[[案例/06-gtg-50029-hacktivists-targeted-european-political-and-affiliated/案例背景调研]]
- 社交文案(785 字):[[案例/06-gtg-50029-hacktivists-targeted-european-political-and-affiliated/社交文案]]
- 信息图:![[案例/06-gtg-50029-hacktivists-targeted-european-political-and-affiliated/gracker信息图-01.png]]
GTG-04001:打断中非共和国境内一场俄罗斯对外信息操纵与干预行动
- 原文:[[案例/07-gtg-04001-disrupting-a-russian-foreign-information-manipulation-a/案例原文]]
- 翻译:[[案例/07-gtg-04001-disrupting-a-russian-foreign-information-manipulation-a/中文翻译]]
- 背景:[[案例/07-gtg-04001-disrupting-a-russian-foreign-information-manipulation-a/案例背景调研]]
- 社交文案(794 字):[[案例/07-gtg-04001-disrupting-a-russian-foreign-information-manipulation-a/社交文案]]
- 信息图:![[案例/07-gtg-04001-disrupting-a-russian-foreign-information-manipulation-a/gracker信息图-01.png]]
GTG-54002:打断一场横跨六大洲的商业「影响力即服务」行动
- 原文:[[案例/08-gtg-54002-disrupting-a-commercial-influence-as-a-service-operatio/案例原文]]
- 翻译:[[案例/08-gtg-54002-disrupting-a-commercial-influence-as-a-service-operatio/中文翻译]]
- 背景:[[案例/08-gtg-54002-disrupting-a-commercial-influence-as-a-service-operatio/案例背景调研]]
- 社交文案(782 字):[[案例/08-gtg-54002-disrupting-a-commercial-influence-as-a-service-operatio/社交文案]]
- 信息图:![[案例/08-gtg-54002-disrupting-a-commercial-influence-as-a-service-operatio/gracker信息图-01.png]]
GTG-84005:打断一个针对马来西亚的商业选举操纵平台
- 原文:[[案例/09-gtg-84005-disrupting-a-commercial-election-manipulation-platform/案例原文]]
- 翻译:[[案例/09-gtg-84005-disrupting-a-commercial-election-manipulation-platform/中文翻译]]
- 背景:[[案例/09-gtg-84005-disrupting-a-commercial-election-manipulation-platform/案例背景调研]]
- 社交文案(802 字):[[案例/09-gtg-84005-disrupting-a-commercial-election-manipulation-platform/社交文案]]
- 信息图:![[案例/09-gtg-84005-disrupting-a-commercial-election-manipulation-platform/gracker信息图-01.png]]
GTG-24015:打断建立在 Claude 上的俄罗斯国家媒体编辑管线
- 原文:[[案例/10-gtg-24015-disrupting-russian-state-media-editorial-pipelines-buil/案例原文]]
- 翻译:[[案例/10-gtg-24015-disrupting-russian-state-media-editorial-pipelines-buil/中文翻译]]
- 背景:[[案例/10-gtg-24015-disrupting-russian-state-media-editorial-pipelines-buil/案例背景调研]]
- 社交文案(887 字):[[案例/10-gtg-24015-disrupting-russian-state-media-editorial-pipelines-buil/社交文案]]
- 信息图:![[案例/10-gtg-24015-disrupting-russian-state-media-editorial-pipelines-buil/gracker信息图-01.png]]
GTG-34001:打断 Claude 上的伊朗国家对齐影响力行动——ICCO、伊斯兰宣传办公室与 Bina 观察站
- 原文:[[案例/11-gtg-34001-disrupting-iranian-state-aligned-influence-operations-o/案例原文]]
- 翻译:[[案例/11-gtg-34001-disrupting-iranian-state-aligned-influence-operations-o/中文翻译]]
- 背景:[[案例/11-gtg-34001-disrupting-iranian-state-aligned-influence-operations-o/案例背景调研]]
- 社交文案(786 字):[[案例/11-gtg-34001-disrupting-iranian-state-aligned-influence-operations-o/社交文案]]
- 信息图:![[案例/11-gtg-34001-disrupting-iranian-state-aligned-influence-operations-o/gracker信息图-01.png]]
GTG-54006:打断一场针对孟加拉国农村、在 Claude 上运行的自动化亲人民联盟假新闻行动
- 原文:[[案例/12-gtg-54006-disrupting-an-automated-pro-awami-league-fake-news-oper/案例原文]]
- 翻译:[[案例/12-gtg-54006-disrupting-an-automated-pro-awami-league-fake-news-oper/中文翻译]]
- 背景:[[案例/12-gtg-54006-disrupting-an-automated-pro-awami-league-fake-news-oper/案例背景调研]]
- 社交文案(782 字):[[案例/12-gtg-54006-disrupting-an-automated-pro-awami-league-fake-news-oper/社交文案]]
- 信息图:![[案例/12-gtg-54006-disrupting-an-automated-pro-awami-league-fake-news-oper/gracker信息图-01.png]]
GTG-84006:打断一场分布式、与伊朗人民圣战者组织 / 伊朗全国抵抗委员会对齐的影响力行动——该行动用共享 AI 智能体假冒真人并在伊朗境内招募
- 原文:[[案例/13-gtg-84006-disrupting-a-distributed-mek-ncri-aligned-influence-ope/案例原文]]
- 翻译:[[案例/13-gtg-84006-disrupting-a-distributed-mek-ncri-aligned-influence-ope/中文翻译]]
- 背景:[[案例/13-gtg-84006-disrupting-a-distributed-mek-ncri-aligned-influence-ope/案例背景调研]]
- 社交文案(805 字):[[案例/13-gtg-84006-disrupting-a-distributed-mek-ncri-aligned-influence-ope/社交文案]]
- 信息图:![[案例/13-gtg-84006-disrupting-a-distributed-mek-ncri-aligned-influence-ope/gracker信息图-01.png]]
GTG-54004:打断肯尼亚一场国内协同不实行为战役
- 原文:[[案例/14-gtg-54004-disrupting-a-domestic-coordinated-inauthentic-behavior/案例原文]]
- 翻译:[[案例/14-gtg-54004-disrupting-a-domestic-coordinated-inauthentic-behavior/中文翻译]]
- 背景:[[案例/14-gtg-54004-disrupting-a-domestic-coordinated-inauthentic-behavior/案例背景调研]]
- 社交文案(809 字):[[案例/14-gtg-54004-disrupting-a-domestic-coordinated-inauthentic-behavior/社交文案]]
- 信息图:![[案例/14-gtg-54004-disrupting-a-domestic-coordinated-inauthentic-behavior/gracker信息图-01.png]]
GTG-84002:打断一场阿联酋主导的影响力行动——目标为穆斯林兄弟会、苏丹冲突与联合国问责机制
- 原文:[[案例/15-gtg-84002-disrupting-a-uae-directed-influence-operation-targeting/案例原文]]
- 翻译:[[案例/15-gtg-84002-disrupting-a-uae-directed-influence-operation-targeting/中文翻译]]
- 背景:[[案例/15-gtg-84002-disrupting-a-uae-directed-influence-operation-targeting/案例背景调研]]
- 社交文案(811 字):[[案例/15-gtg-84002-disrupting-a-uae-directed-influence-operation-targeting/社交文案]]
- 信息图:![[案例/15-gtg-84002-disrupting-a-uae-directed-influence-operation-targeting/gracker信息图-01.png]]
GTG-54009:打断一个用 Claude 给伊朗与波斯湾用户社交媒体账号建档的商业监控平台
- 原文:[[案例/16-gtg-54009-disrupting-a-commercial-surveillance-platform-using-cla/案例原文]]
- 翻译:[[案例/16-gtg-54009-disrupting-a-commercial-surveillance-platform-using-cla/中文翻译]]
- 背景:[[案例/16-gtg-54009-disrupting-a-commercial-surveillance-platform-using-cla/案例背景调研]]
- 社交文案(801 字):[[案例/16-gtg-54009-disrupting-a-commercial-surveillance-platform-using-cla/社交文案]]
- 信息图:![[案例/16-gt
...[local evidence truncated]...